Crash Instagram Direct (without victim interaction)
One Instagram note with an unknown style value crashed Direct for everyone who saw it, with no action from the victim. Meta fixed it in March 2024.
On this page
Instagram notes are short messages that appear at the top of the Direct inbox for people you follow back. I found that the server accepted a note style the Android app did not know how to draw. One such note made Direct crash every time a mutual follower opened it, with no tap from them. Meta fixed it in March 2024.
What does Instagram promise about notes?
A note is a short message you share with followers you follow back, or with your Close Friends list. It sits in a row above your chats, so the inbox has to draw it before you can reach any conversation. A note should be harmless decoration on top of your messages. It should never stop you from reading them.
How did one note crash Direct?
In plain words
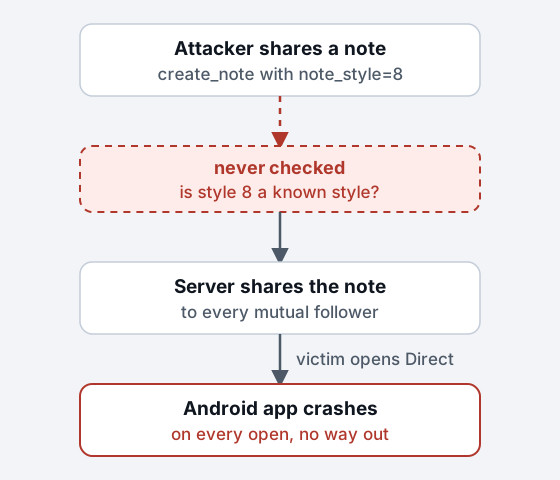
Each note carries a small number that tells the app which look to use, such as plain text or video. The app knows a fixed set of these numbers. I sent a number outside that set. The server saved it without complaint, and the app crashed when it tried to draw a look it had never heard of.
What happened
Sharing a note sends one request. The note_style field picks the note’s look, and audience picks who sees it.
POST /api/v1/notes/create_note/ HTTP/1.1
Host: i.instagram.com
Content-Type: application/x-www-form-urlencoded

note_style=0&text=test
&_uuid=<DEVICE_UUID>&audience=0
(The body is wrapped for narrow screens.) I intercepted this request and changed note_style from 0 to 8. The text can be anything, even empty.
POST /api/v1/notes/create_note/ HTTP/1.1
Host: i.instagram.com
Content-Type: application/x-www-form-urlencoded

note_style=8&text=
&_uuid=<DEVICE_UUID>&audience=0
The server accepted the note and shared it as normal. On the victim’s side, opening Direct crashed the Android app, every time. The note sits in the row the inbox draws first, so the victim never reached a chat. There was no setting to hide that one note, so the victim had no way out while it stayed up.
Setting audience=1 limited the note to my Close Friends list, which let me choose exactly who was hit.
Reproduction
You need two Android test accounts you own that follow each other, and a proxy that can edit app traffic.
- From the attacker account, share a note and intercept
create_note. - Change
note_styleto8. Leavetextempty or put anything in it. - Keep
audience=0for all mutual followers, or set1for Close Friends only. - Forward the request.
- On the victim account, open Direct. The app crashes on every open.
What was the impact?
Anyone could take away Direct on Android from the people they follow back, without any action from those people. It did not leak data or take over accounts. It removed access to private messages, which for many people is the main reason they open Instagram.
Scope and limits
Confirmed:
- Direct crashed on every open for a mutual follower, tested on my own accounts with app version 319.0.0.0.64.
- The server accepted
note_style=8and an emptytext. audience=1narrowed the crash to Close Friends.
Not confirmed:
- Behaviour on iOS or the web. I tested only the Android app.
- What happens after the note expires on its own. I did not measure how long the crash lasted past that point.
Why did it happen?
The server trusted the client to send a style the app knows. note_style is a small fixed list, but create_note stored any number and passed it to every viewer. The Android app then met a value it had no layout for and failed hard instead of skipping the note. That is Improper Input Validation: one unchecked field turned into a crash on someone else’s phone.
How was it fixed?
Meta confirmed the issue was patched as of 2024-03-18, and I checked it myself on 2024-03-20. The usual fix for this kind of bug has two halves. The server rejects any value outside the known list, and the client skips content it cannot draw instead of crashing.
What can developers learn?
- Check enumerated fields against an allowlist on the server.
- Remember that what one user saves is rendered on other users’ devices. A bad value becomes their problem.
FAQ
Was anyone’s data exposed?
No. The bug crashed the app; it did not read or leak data.
Who could be affected?
Android users who followed the attacker back, or who were on the attacker’s Close Friends list.
What should users do now?
Nothing. The fix is on Meta’s side.
What was the root cause?
The note API stored a style number the app did not know, and the app crashed instead of ignoring it.
Timeline
- 2024-02-16: Reported with step-by-step reproduction.
- 2024-02-22: Sent to the product team.
- 2024-02-28: Meta awarded a $1,500 bounty.
- 2024-03-18: Meta confirmed the issue was patched.
- 2024-03-20: I verified the fix.
- 2026-10-26: Write-up published.